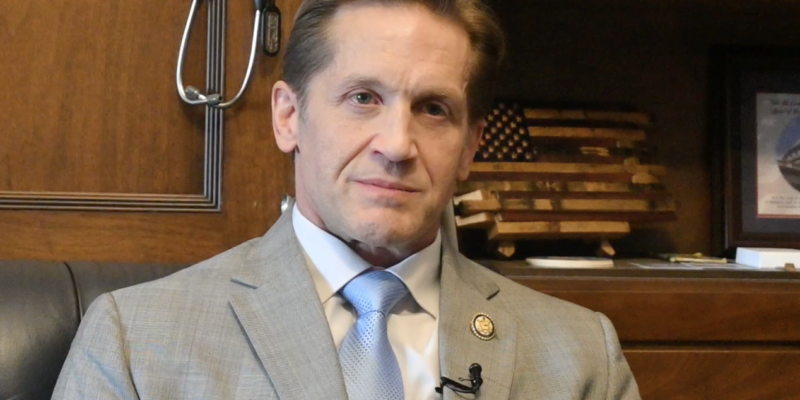

Representative Rich McCormick (R-GA) recently introduced the Common-Sense Cloud Security Act to strengthen America’s cloud cybersecurity by issuing new directions to the National Institute of Standards and Technology (NIST).
What does the Common-Sense Cloud Security Act require of NIST? The bill requires NIST to develop updated standards to protect sensitive data, prevent cyberattacks, and secure critical infrastructure.
NIST must also work with federal cybersecurity officials, cloud service providers, critical infrastructure operators, and academic experts to address vulnerabilities in cloud environments, including through the use of artificial intelligence to detect suspicious activity.
What Rich McCormick had to say:
- Via Press Release: “In 2026, nearly everything we do relies on the cloud. From our financial information and medical records to our national security and critical infrastructure, our most sensitive information is stored and accessed through cloud-based systems.”
- Continued: “Our adversaries, including China, are constantly looking for ways to exploit vulnerabilities, launch cyberattacks, and steal sensitive American information. We cannot afford to leave Americans exposed to these threats. The Common-Sense Cloud Security Act strengthens our cyber defenses, protects sensitive information, and keeps America one step ahead of our adversaries.”
- Via his Official X: “As technology advances, so do the threats to Americans’ sensitive information. My Common-Sense Cloud Security Act will modernize cybersecurity standards, strengthen defenses against cyberattacks, and encourage AI-powered threat detection. Our cybersecurity must keep pace with the technology we depend on.”
Key provisions of the bill:
- Require NIST to report to Congress on federal implementation, private-sector adoption challenges, and recommendations to improve cloud cybersecurity.
- Update FedRAMP to align with new cloud security standards and strengthen cybersecurity disclosures for federal cloud providers.
- Establish a voluntary, tiered Cloud Security Certification Program using independent, accredited testing laboratories.
- Encourage the use of artificial intelligence to detect unusual or suspicious activity in cloud environments.
- Develop a methodology to assess the scope of cloud security breaches and how far a compromise could spread.